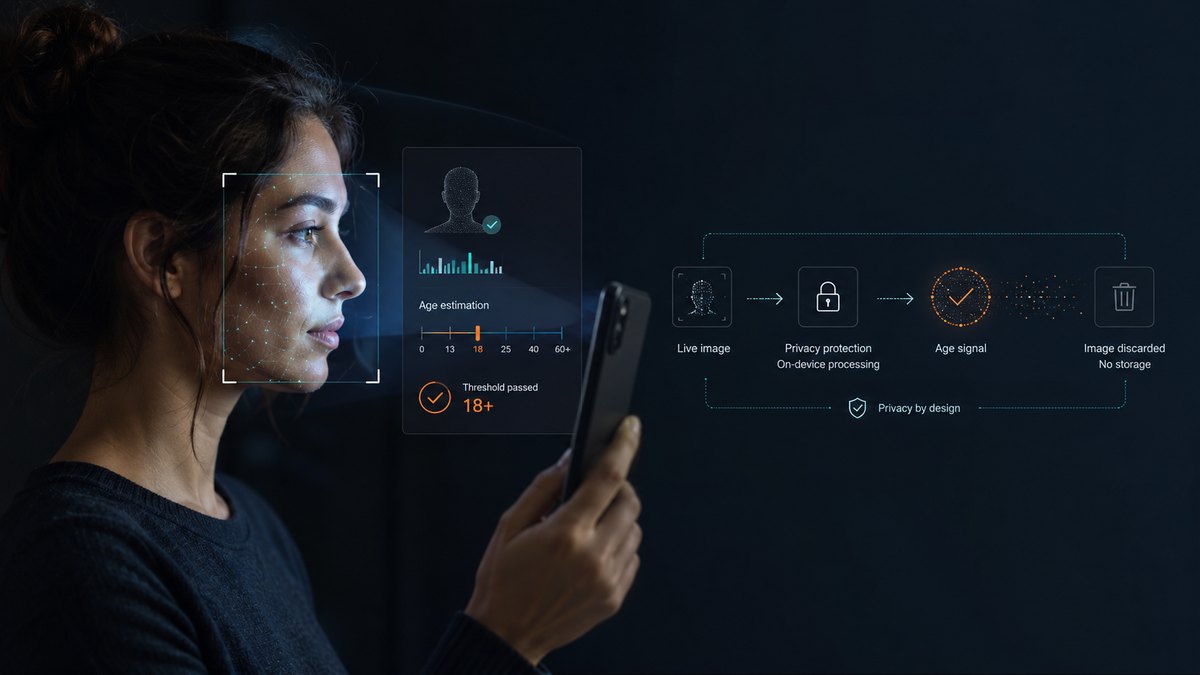
Age checks used to be a checkbox that asked users to confirm they were over 18, a control everyone involved understood to be theater. In 2026, that theater is a legal liability. Regulators on three continents now require platforms to know, with demonstrable confidence, whether a user is a child, and to prove it without hoarding identity documents. This is the problem age estimation AI was built for: software that estimates a person’s age range from a live face image, returns an over-or-under decision for a threshold like 13, 16, or 18, and does it without ever establishing who the person is.
The distinction between estimating age and verifying identity is the technical heart of the whole compliance conversation. Facial age estimation is a face analytics task, not a face recognition task. The model looks at a single image or video frame and predicts an age, typically measured by mean absolute error in independent testing. It does not match the face against any database, and in privacy-preserving deployments the image is processed and discarded rather than retained. That architecture is precisely what makes the approach defensible under privacy regimes that would punish a platform for warehousing scans of children’s identity cards.
Accuracy claims in this market should be read the way auditors read them: against independent benchmarks, not marketing pages. The National Institute of Standards and Technology runs public evaluations of age estimation software and reports error rates per vendor and per demographic group, which gives compliance teams a rare luxury in AI procurement, a neutral scoreboard. Vendors participating in that testing publish their results; developers such as ROC document NIST-evaluated performance across their vision and biometrics portfolio, which is the level of evidence a regulator or auditor will expect to see in a due-diligence file.
In This Article:
The regulatory wave driving adoption
The compliance pressure is no longer hypothetical, and it is arriving from multiple directions at once. The UK’s Online Safety Act requires services hosting content harmful to children to deploy what the regulator calls highly effective age assurance, with enforcement underway since 2025. Australia’s minimum-age law for social media pushed platforms to detect and remove under-16 accounts. In the United States, COPPA governs data collected from children under 13, and a growing list of state laws requires online age verification for adult content, social media accounts for minors, or app store downloads, with the map of obligations changing session by session.
The common thread across these regimes is that self-declared birthdates no longer satisfy anyone. Platforms need a method that produces an auditable age signal at account creation or content access, works at consumer scale, and does not create a new privacy scandal in the process of preventing one.
Where estimation fits among age assurance methods
Facial age estimation is one tool in a toolbox, and mature compliance programs usually deploy it in combination with others. The trade-offs sort cleanly.
| Method | Friction for the user | Privacy exposure | Assurance strength |
| Self-declaration | None | None | Minimal; easily falsified |
| ID document check | High; requires a document | High; identity data collected | Strong, tied to identity |
| Facial age estimation | Low; one selfie, seconds | Low when images are not retained | Strong for threshold decisions, no identity involved |
| Parental consent flows | Moderate | Moderate | Depends on verifying the parent |
The pattern most platforms converge on is a waterfall. Estimation runs first because it is fast and anonymous; the clear cases pass or fail immediately. Users near the threshold, where model error could matter, are routed to a fallback such as a document check. Regulators in several jurisdictions have explicitly endorsed this buffer-zone design because it concentrates stronger verification where the uncertainty actually is.
What good age recognition software looks like
Procurement teams evaluating age recognition software in 2026 should hold every candidate to five checks. First, independent testing: the vendor should appear in NIST’s age estimation evaluation with published error rates, and the buyer should read the demographic breakouts, not just the headline number. Second, liveness: an age check that can be fooled by a photograph of an older sibling is a control that exists only on paper, so presentation attack detection belongs in the same pipeline. Third, data handling: images should be processed transiently, with no biometric retention by default, and the data flow should be documented well enough to survive a records request. Fourth, threshold configurability: a platform serving multiple jurisdictions needs different age gates and buffer zones per market. Fifth, graceful failure: poor lighting, camera refusal, or an inconclusive score should route to an alternative method rather than silently blocking or admitting the user.
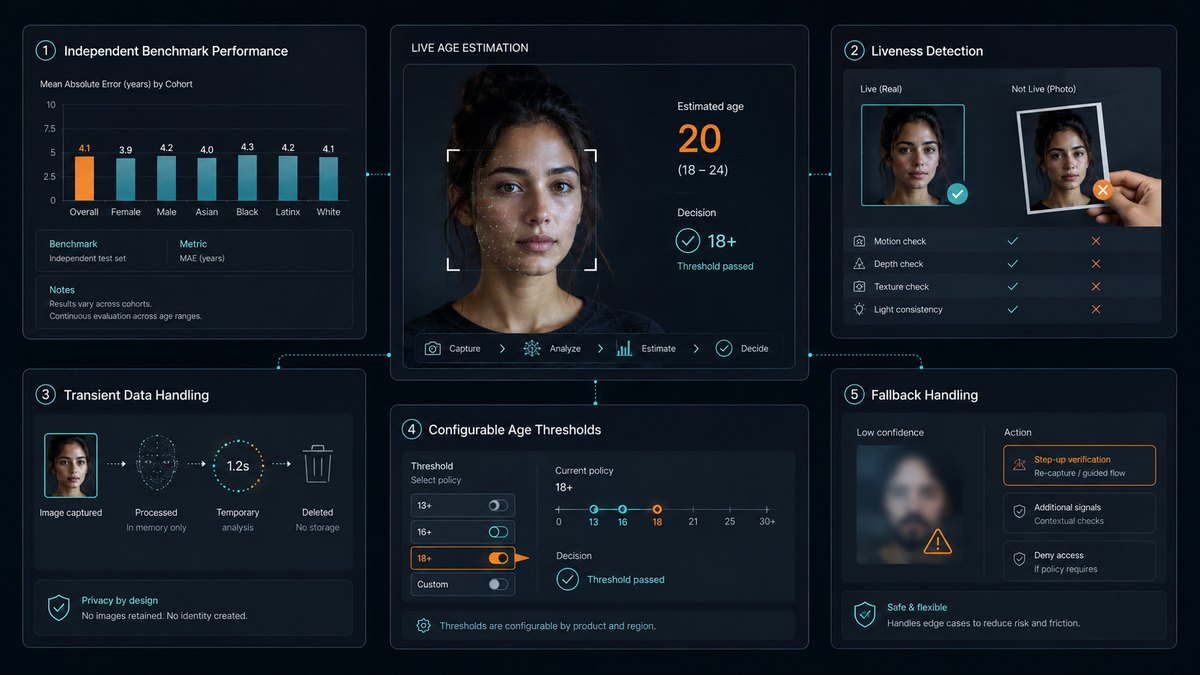
Bias deserves its own sentence rather than a footnote. Estimation error is not uniform across ages, and a system tuned only on adult faces can drift at exactly the age bands the law cares about. The responsible posture is the one independent testing enables: measure error by cohort, publish it, buffer for it, and never claim the problem is solved.
Practical rollout sequence
- Map obligations by market: which age thresholds, which content types, which laws, and which deadlines apply where you operate.
- Choose the waterfall: estimation first, with document verification or another fallback for the buffer zone near each threshold.
- Pilot with your real user base and measure pass rates, fallback rates, and completion drop-off before committing to a vendor.
- Write the data protection assessment up front, covering retention, lawful basis, and children’s data specifically.
- Log every age decision with its method and confidence band, because the audit will ask not just what you decided but how.
The bottom line
Online age verification stopped being optional the moment regulators started fining platforms for knowing too little about who their youngest users are. Facial age estimation has become the workhorse of compliance programs because it answers the narrow question the law asks, over or under, without collecting the identity data the law simultaneously tells platforms to minimize. Independent benchmarks make the market unusually accountable, and the published age estimation results from American vision AI developers like Rank One Computing show how far threshold accuracy has come; the compliance teams that pair that capability with honest buffer zones and documented fallbacks are the ones that will pass their audits without alienating their users.